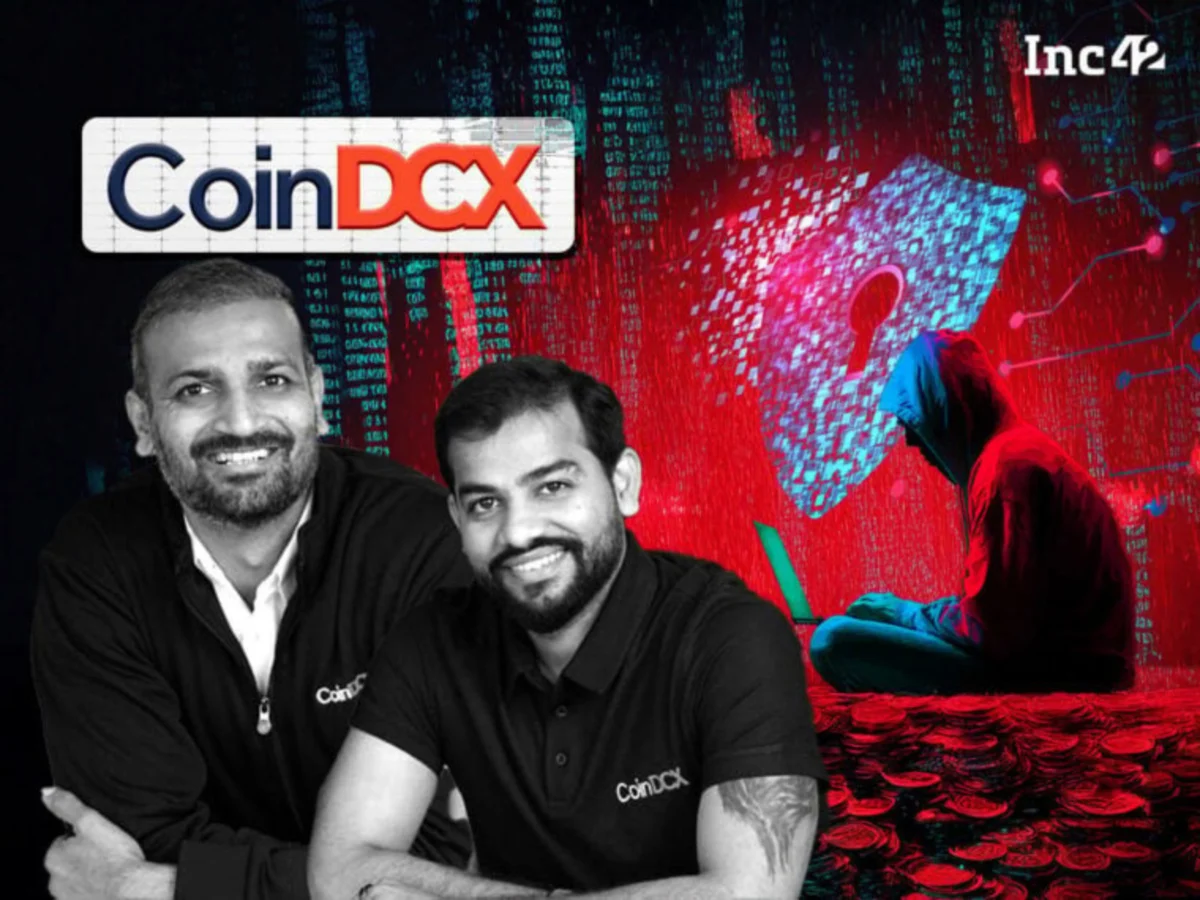
The Indian cryptocurrency landscape was rattled this week as CoinDCX, one of the nation’s most prominent digital asset exchanges, admitted to experiencing “operational losses” resulting from a breakdown in its internal deposit-security protocols. The disclosure comes on the heels of a frantic period of online speculation, during which blockchain sleuths raised alarms regarding suspicious activity involving wallet addresses previously linked to the exchange.
While CoinDCX maintains that its active infrastructure remains uncompromised and that no user assets were lost in this latest incident, the admission highlights the precarious nature of maintaining security in the wake of a major cyberattack. The incident serves as a sobering reminder of the "long tail" of security vulnerabilities that persist even after an exchange implements major system overhauls.
Main Facts: The Anatomy of the Operational Failure
The core of the issue lies in a technical oversight concerning "legacy" or "discontinued" wallet addresses. Following a significant security breach in July 2025, in which CoinDCX lost approximately $44 million, the exchange decommissioned a vast number of wallet addresses that had been exposed to the attackers.
Despite proactive notifications sent to users instructing them to cease deposits to these old addresses and instead utilize updated, secure addresses generated through the CoinDCX platform, some users continued to send funds to the compromised channels. Under normal operating conditions, CoinDCX utilizes an automated "sweeping" mechanism designed to monitor these discontinued addresses, collect any incoming deposits, and move them into the company’s secure, segregated cold storage.
However, the exchange confirmed that this automated sweeping process experienced a critical failure. During the window of this failure, funds sent by users to these obsolete addresses were effectively "lost" to the company’s internal tracking systems. By the time the technical team identified the failure, the assets had been diverted. CoinDCX has stated that it has since absorbed the financial impact of these losses, ensuring that all affected customers have had their balances correctly credited in full.
Chronology of Events: From July Breach to Recent Speculation
To understand the current situation, one must look back at the trajectory of the exchange’s security challenges throughout 2025.
The July 2025 Crisis
In July 2025, CoinDCX suffered a major security incident involving an internal operational account used to provide liquidity on a partner exchange. Attackers managed to siphon off $44 million in assets. At the time, CoinDCX acted quickly to contain the damage, asserting that the stolen assets were drawn from the company’s treasury rather than customer accounts. They launched a recovery bounty program and implemented a comprehensive audit of all wallet infrastructure.
The Rise of Blockchain Vigilantism
Fast-forwarding to the present, the recent controversy began when independent blockchain investigator "Darcy" posted findings on X (formerly Twitter). Darcy flagged the movement of approximately $16 million in cryptocurrency from wallets previously associated with CoinDCX. These funds were observed being split across multiple addresses and subsequently funneled into deposit addresses at major global exchanges, including Binance, OKX, and Gate.io.
The Initial Denial
In the immediate aftermath of these social media posts, CoinDCX issued a sharp rebuttal. The exchange dismissed the claims as "misleading," asserting that the flagged addresses had been inactive since the July 2025 hack. CEO Sumit Gupta personally intervened, clarifying that the exchange had performed a deep-dive forensic analysis of its current central and user wallet addresses and found no evidence of unauthorized transfers. He suggested that the hackers were likely "reusing" the old, public-facing addresses to create a false narrative of a fresh breach.
The Pivot to Disclosure
Following the pressure from the community and further internal investigation, the company performed a U-turn. Recognizing that the public skepticism was rooted in genuine technical discrepancies, CoinDCX issued a follow-up statement acknowledging the operational failure. They admitted that while the core exchange systems were secure, the specific "sweep" process for legacy addresses had failed, allowing assets to be siphoned off by malicious actors who were monitoring those specific, discarded addresses.
Supporting Data and Technical Context
The security of a centralized exchange relies on a "Cold-Hot-Warm" wallet architecture. Active (hot) wallets are used for day-to-day liquidity and user withdrawals, while cold wallets are kept offline to prevent remote hacking.
The issue faced by CoinDCX highlights the danger of "Address Poisoning" or simply the "Legacy Address Trap." When an exchange changes its wallet infrastructure, it effectively abandons old addresses. However, on a public blockchain, those addresses remain visible and functional. If a malicious actor possesses the private keys—or in this case, if the exchange’s automated monitoring fails to secure the incoming flow—the assets sent to those addresses are effectively redirected to an attacker’s wallet.
- Financial Impact: While CoinDCX has not provided a specific dollar amount for the current operational loss, the $16 million figure cited by blockchain investigators remains the primary point of public focus.
- Asset Segregation: CoinDCX continues to emphasize that its primary user asset reserves, held in segregated cold wallets, were entirely untouched by this incident.
- Trading Continuity: Unlike the July incident, which required significant containment measures, this recent failure did not necessitate a suspension of trading or a halt to platform operations.
Official Responses and Accountability
The response from CoinDCX leadership has been a blend of transparency regarding the technical failure and a firm stance on the safety of the platform.
CEO Sumit Gupta’s Perspective:
Sumit Gupta has remained the face of the communication strategy, emphasizing that the exchange takes full responsibility for the funds. "We have absorbed the losses," Gupta noted, aiming to reassure the retail user base that the exchange’s balance sheet remains robust enough to cover these types of operational errors.
The Shift in Tone:
Industry observers have noted that CoinDCX’s shift from initial denial to full admission is a growing trend in the crypto sector. As blockchain transparency tools become more sophisticated, exchanges can no longer rely on obfuscation. By acknowledging the failure, CoinDCX appears to be attempting to maintain its regulatory standing and user trust, even if the admission has temporarily damaged its reputation for technical perfection.
Implications: The Future of Exchange Security
The fallout from this incident has broader implications for the Indian crypto market and the global exchange ecosystem.
1. The Cost of "Technical Debt"
Exchanges often accumulate "technical debt"—a backlog of legacy systems, old API integrations, and obsolete wallet addresses. The CoinDCX incident serves as a case study for the risks inherent in failing to properly decommission infrastructure. Proper "sunsetting" of legacy wallet addresses is as vital as the security of new ones.
2. The Power of On-Chain Forensics
The fact that a third-party investigator was able to identify the suspicious movement of funds before the exchange officially disclosed the issue underscores the transparency of public ledgers. For exchanges, this means that silence is no longer an option. Future security strategies will likely need to integrate real-time blockchain monitoring that is accessible to both the exchange and, in some capacity, the user base.
3. Regulatory Scrutiny
In India, where the regulatory environment for digital assets is already cautious, such incidents are likely to draw the attention of bodies like the Financial Intelligence Unit (FIU). Exchanges will likely face more stringent requirements regarding their "Proof of Reserves" and the auditing of their wallet management protocols.
4. User Behavior and Education
Despite the exchange’s efforts, the fact that users continued to deposit into compromised addresses points to a gap in user education. Exchanges must find ways to make "deposit address changes" more intrusive and unavoidable, perhaps by disabling old addresses at the smart-contract level rather than relying on notifications.
Conclusion
CoinDCX’s recent admission of operational losses marks a challenging chapter in its ongoing effort to recover from the turbulence of 2025. While the exchange has successfully prevented a systemic collapse and protected its users’ balances, the incident highlights the fragility of internal processes when faced with the persistent threats of the crypto-underworld.
As the exchange looks to move forward, the focus will likely shift toward radical transparency and a more aggressive approach to technical maintenance. For the broader industry, the incident serves as a necessary, albeit painful, reminder: in the world of decentralized finance, security is not a "set-and-forget" configuration, but a constant, evolving battle against both hackers and one’s own legacy infrastructure.
For now, CoinDCX remains operational, and its users remain whole. However, the shadow of the July 2025 hack continues to loom large, proving that in the digital asset space, the past is never truly behind you until every last door has been securely locked.